
A Practical Zero Trust Architecture for AI Agents
AI agents that can act on systems need more than a shared service account. A Zero Trust design gives each run a verifiable identity, short-lived authority, policy checks…
23 articles
Security changes, vulnerabilities and practical resilience without turning every update into panic or theatre.
15 articles · authority 65/100
AI agents that can act on systems need more than a shared service account. A Zero Trust design gives each run a verifiable identity, short-lived authority, policy checks…

Windows Server 2025 tightens defaults that affect authentication, directory traffic and shared storage. Microsoft’s OSConfig provides a baseline starting point, but the practical question is where stricter LDAP, Kerberos and SMB behaviour will break legacy apps and workflows before you roll it out.

AI agents that can act on systems need more than a shared service account. A Zero Trust design gives each run a verifiable identity, short-lived authority, policy checks at the tool boundary and an auditable record of consequential actions.

VMware Telco Cloud Platform 5.2 frames Kubernetes upgrades, policy drift, scoped infrastructure access and registry maintenance as telecom security controls. Its practical value depends on operators proving those controls across complex multi-vendor CNF estates.
The decision is less about “which endpoint tool is best” than which control plane you want to live with. Defender for Endpoint is usually the cleaner fit if you already run Microsoft 365, Intune, Entra and Sentinel. CrowdStrike can better match an endpoint-first operating model.

A regulated Azure Local deployment needs more than local workloads. This blueprint sets out how to define management, identity, network, key and evidence boundaries, then map them to repeatable controls and audit artefacts.

Immutable backup can stop protected recovery data being changed or deleted before its retention deadline. But its value depends on the enforcement mechanism, administrative overrides, retention period and whether the organisation can restore a clean copy.
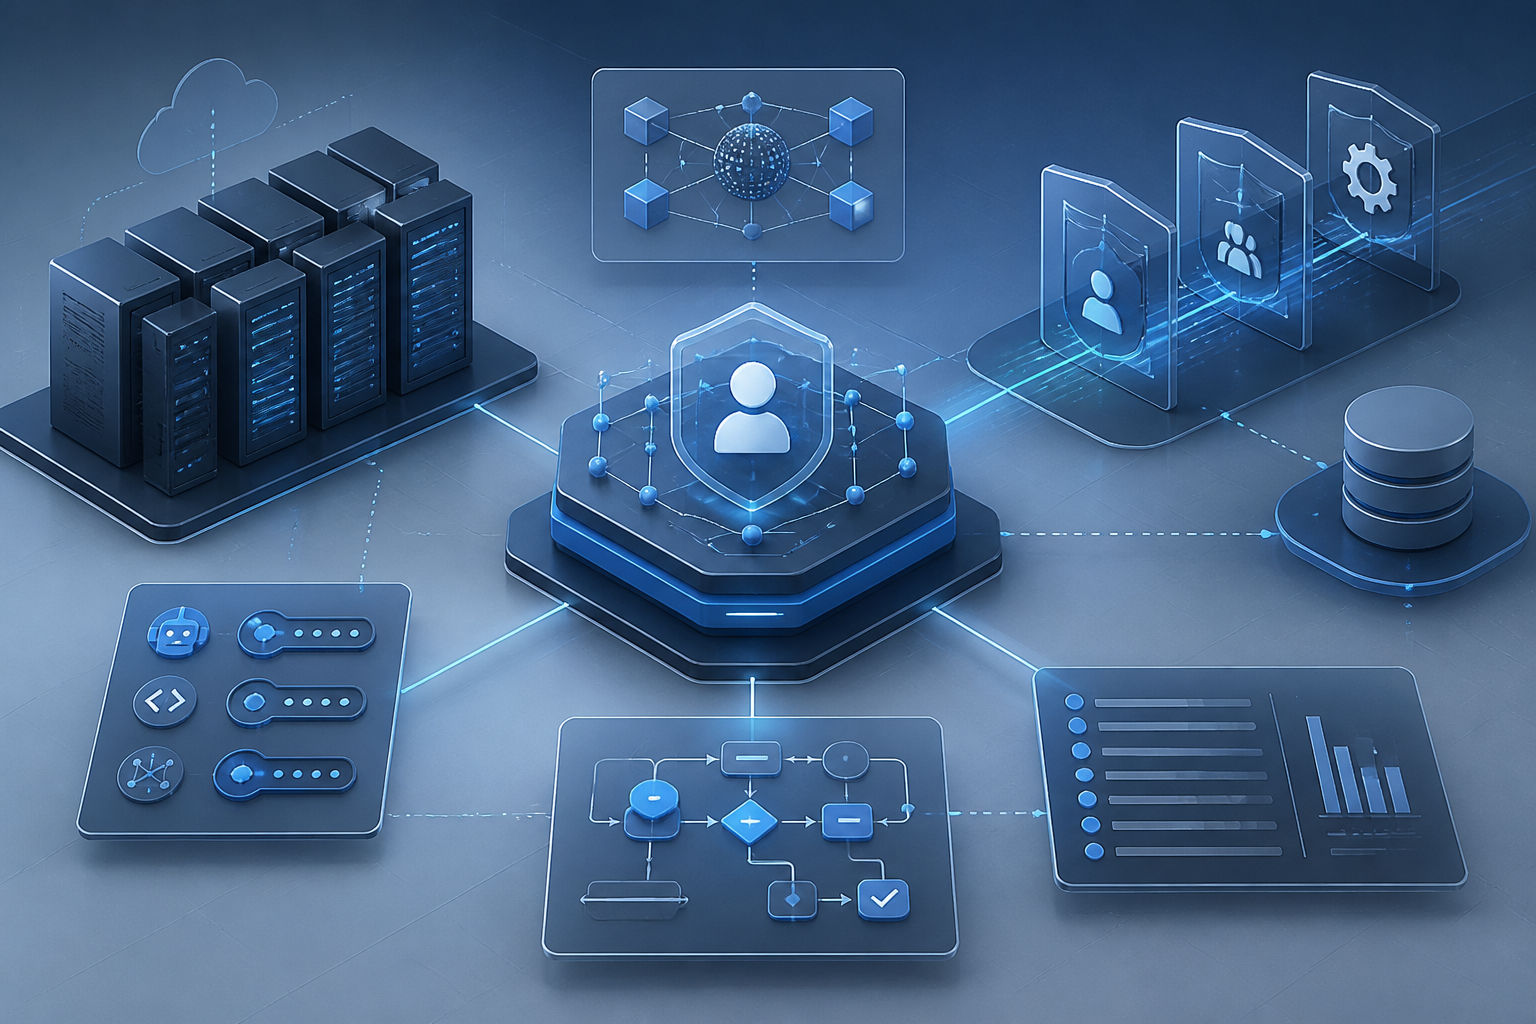
The enterprise rush to deploy AI agents is running into a familiar problem in a new form: identity. If an agent can act, call tools, move data or trigger workflows, it needs a proper identity model, not a vague service account and a hope that logs will be enough. That shifts the discussion from ‘what can the model do?’ to ‘what can this agent prove it is allowed to do, and how is that enforced?’

Critical unauthenticated code execution in specified Silicon One-based Cisco Nexus 9000 switches can give a reachable attacker root privileges and reload the device. Operators should urgently establish exposure, restrict access and upgrade using Cisco’s platform-specific guidance.
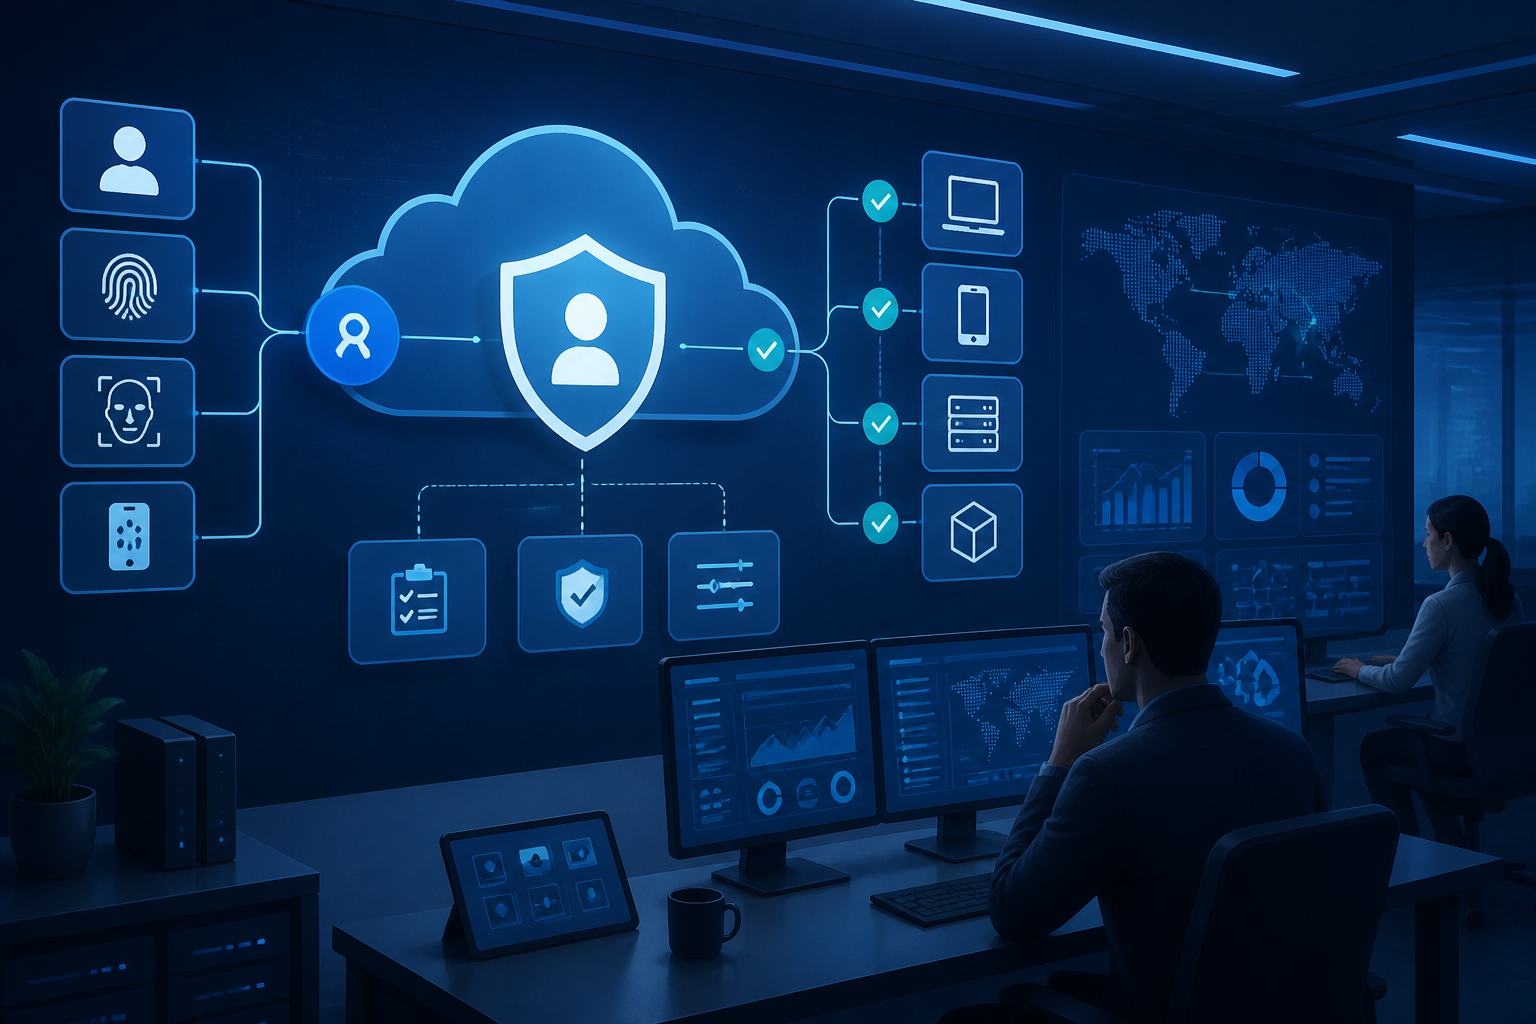
If you are tightening up Microsoft Entra ID security, the first wins are usually not exotic: they are the controls that reduce password abuse, shrink admin exposure, and stop legacy sign-in paths from becoming an easy route in. The trick is to turn on the right controls in the right order, without breaking sign-in for the people who keep the business running.

Microsoft is steering Entra ID away from SMS and voice MFA and towards passkeys. The shift is security-led, but it’s operationally risky: recovery, Conditional Access interactions, legacy apps, and helpdesk load can all change the outcome.